••
AI Cybersecurity in 2026: How Artificial Intelligence Is Changing Online Security
Artificial intelligence is transforming cybersecurity in 2026. Learn how AI improves threat detection while creating new risks such as deepfake fraud, prompt injection, AI-powered phishing, and over-permissive agents.
Share Article:
Share:
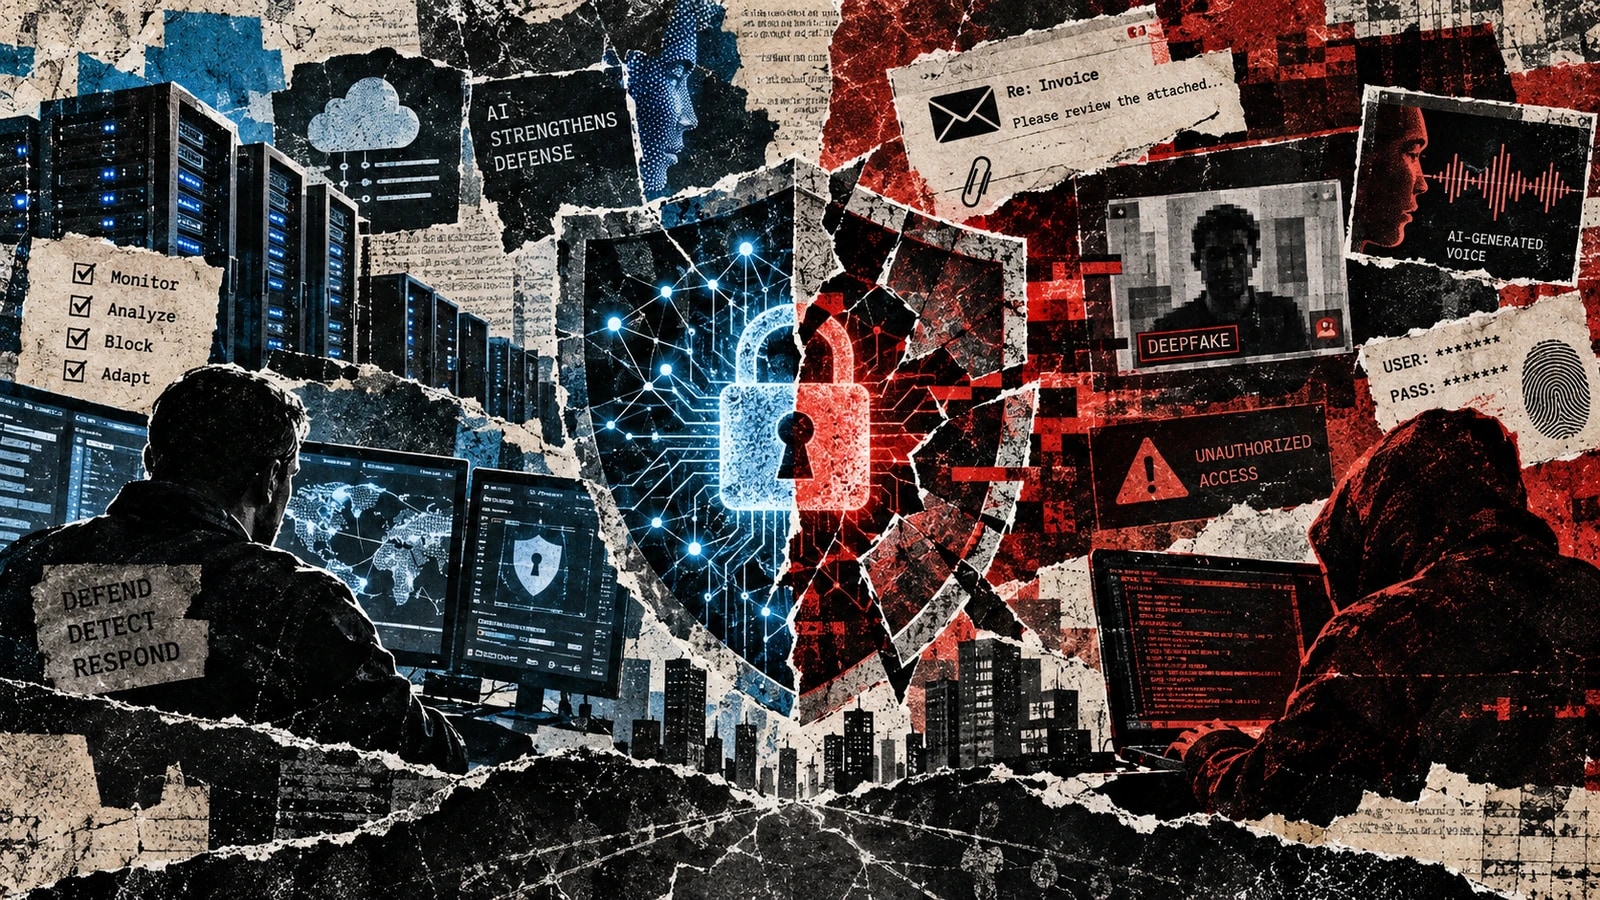
Artificial intelligence has pushed cybersecurity into a faster cycle. Detection, response, and evasion now evolve in shorter bursts, because both defenders and attackers can use models to automate work that once took analysts hours.
Security teams are using AI to sort alerts, rank suspicious activity, and triage logs across cloud, endpoint, and identity systems. That matters because modern enterprise environments generate far more signals than human operators can review in real time. When a system can group related events and surface the most likely incident first, it reduces the chance that a low-volume intrusion stays hidden.
Attackers benefit from the same acceleration. They can use AI to draft phishing messages that read more naturally, adapt lures for different targets, and test payload variations at scale. The result is not a single new threat, but a larger volume of convincing attempts that are harder to dismiss at a glance.
A Real Case That Shows What's at Stake
The clearest illustration of how far this has already gone is the Arup case. In January 2024, a finance employee at the engineering firm's Hong Kong office joined a video call with people who appeared to be the company's CFO and several colleagues. Every face and every voice on that call was AI-generated. Believing the meeting was real, the employee authorized 15 separate wire transfers totaling $25.6 million before the fraud was discovered — and the funds were never recovered.
The scale of that single incident is unusual, but the pattern behind it isn't. The FBI's Internet Crime Complaint Center logged over $893 million in reported losses tied to AI-related fraud in 2025 alone, and voice-cloning tools that once required specialist skills can now produce a convincing clone from just a few seconds of audio pulled from a public video or voicemail. That's part of why security teams are rethinking identity verification, not just spam filters.
Where AI Fits Inside the Security Stack
Most AI security tools do not replace the full stack. They sit on top of existing telemetry and help make sense of it.
The usual architecture starts with data collection from identity logs, email gateways, endpoint agents, cloud workloads, and network sensors. That data flows into a model layer that scores risk, classifies patterns, or detects anomalies. A response layer then decides whether to alert an analyst, open a ticket, isolate a device, or request additional verification.
This setup works best when the model is tightly connected to context. A login from a new country may be harmless for one employee and suspicious for another. A file movement inside a backup workflow may look abnormal in isolation, but be routine in a scheduled job. AI improves when it can combine signals, not just inspect one event at a time.
The tradeoff is that model output still depends on data quality. If telemetry is incomplete, stale, or biased toward certain asset types, the system may miss the very activity it is meant to catch. That is why many security teams keep human review in the loop for high-impact actions.
The Attack Surface Moves Into the Model Itself
AI does not simply change the tools defenders use. It creates a new class of security issues around the model, the prompt layer, and the data feeding both.
One risk is prompt injection, where hostile text tries to influence an assistant that is reading emails, documents, or web pages. Another is data poisoning, where attackers contaminate training or fine-tuning inputs so the model learns a harmful pattern. A third is model abuse through over-permissive connectors, when an assistant can access systems or records it should not reach.
These are not abstract problems. If an AI agent can read a mailbox, open a file, and trigger a workflow, then a malicious instruction hidden inside a message may become an operational issue rather than a simple content-filtering failure. The security model has to assume that input is untrusted, even when it appears to come from a normal business channel.
That is changing how teams design controls. Least privilege now applies to models and agents as much as to employees. Access should be limited by role, task, and data sensitivity. Logging matters too, because teams need to reconstruct what the model saw, what it did, and why it chose a given response.
Detection Is Getting Smarter, and Less Predictable
Traditional security analytics relied heavily on signatures and fixed thresholds. AI systems can go further by learning patterns of behavior, then spotting deviations that a rule engine would miss.
That helps in cloud environments, where identities, APIs, and workloads change constantly. It also helps in fraud and account takeover detection, where an attacker may use legitimate credentials but behave in a way that differs from the usual user profile.
Still, model-based detection has limits. False positives can rise when normal behavior changes, such as during migrations, mergers, or seasonal business cycles. False negatives remain possible when attackers mimic legitimate activity. A detection engine that is too sensitive creates alert fatigue, while one that is too conservative lets threats pass.
The practical answer is calibration. Teams are increasingly blending AI scores with rules, threat intelligence, and asset criticality. A suspicious login on a test machine should not get the same treatment as one on a payments admin account. Context decides priority.
Why Generative AI Raises the Stakes for Identity
Identity is now one of the clearest pressure points in cybersecurity. Generative AI has lowered the cost of making messages, voice clips, and fake support interactions look credible.
That creates a tougher environment for phishing resistance, business email compromise prevention, and help-desk verification. A poorly designed verification process can be gamed by a convincing script or a synthetic voice sample. As a result, organizations are moving toward stronger out-of-band checks — like calling a known number back instead of trusting caller ID — along with device binding and step-up authentication when risk rises.
The same logic applies to internal controls. If an AI assistant can prepare a password reset request or summarize a sensitive ticket, the workflow needs to know whether the requester is authorized and whether the request itself is ordinary. Authentication alone is not enough. Authorization, logging, and approval boundaries have to follow the action.
The Cost of Trusting Automation Too Much
AI promises speed, but speed can backfire when teams trust automation blindly.
A model may confidently flag a benign event as hostile, or miss a slow-moving intrusion because the pattern does not resemble prior incidents. It may also generate explanations that sound plausible without being fully accurate. Security operators need evidence, not just a score.
That is why the best deployments tend to pair AI with controls that are old-fashioned in the best sense. Segmentation, multifactor authentication, patch discipline, immutable logs, and backup recovery still matter. AI can improve the odds of spotting trouble earlier, but it does not remove the need for strong basics.
AI Risks and Matching Controls at a Glance
| AI-driven riskWhat it looks likeTypical control | ||
|---|---|---|
| Voice/video deepfake fraud | Cloned "executive" requesting an urgent wire transfer | Out-of-band callback to a known number, dual approval |
| Prompt injection | Hidden instructions inside an email or document read by an AI agent | Treat all input as untrusted, limit agent permissions |
| Data poisoning | Corrupted training or fine-tuning data | Vet data sources, monitor for unexplained model drift |
| AI-written phishing | Natural-sounding, personalized lures at scale | Behavioral email filtering, ongoing user training |
| Over-permissive AI agents | An assistant with access to more systems than its task needs | Least-privilege access, detailed action logging |
What Decision Makers Should Watch Next
For business and technology leaders, the near-term issue is governance. AI security tools should be tested against real workflows, real data, and real failure cases before they are given broad authority.
That means checking how models behave when telemetry is incomplete, how quickly analysts can override an automated action, and whether logs provide enough detail for later review. It also means treating AI vendors like any other critical supplier. Access rights, model update practices, and incident reporting should be reviewed as part of procurement and security audits.
The organizations that will do best are the ones that treat AI as an amplifier, not a substitute. Used carefully, it can shorten response times and improve detection quality. Used carelessly, it can enlarge the blast radius of a mistake.
This article is for general informational purposes and does not constitute professional cybersecurity or legal advice. Organizations should consult a qualified security professional before implementing controls based on the information above.
Sources
- National Institute of Standards and Technology, AI Risk Management Framework: https://www.nist.gov/itl/ai-risk-management-framework
- National Institute of Standards and Technology, Cybersecurity Framework: https://www.nist.gov/cyberframework
- CISA, AI and Cybersecurity guidance and resources: https://www.cisa.gov/topics/artificial-intelligence
- FBI Internet Crime Complaint Center (IC3), 2025 Internet Crime Report
- Google Cloud, Securing generative AI applications: https://cloud.google.com/security/ai
Frequently Asked Questions
Can AI security tools replace human analysts?
No. AI is best at sorting and prioritizing large volumes of alerts, but high-impact decisions — like isolating a system or approving a large financial transaction — still benefit from human review, especially since models can be confidently wrong.
What is prompt injection, in plain terms?
It's when hidden instructions are planted inside content an AI assistant reads — like an email or document — hoping the AI will follow them instead of the user's actual request. Well-designed systems treat all incoming content as untrusted by default.
Do small businesses really need to worry about AI-driven fraud, or is this mainly a large-enterprise problem?
Both are targets. High-dollar deepfake fraud tends to make headlines at large companies, but AI-written phishing and voice-cloning scams are cheap enough that smaller businesses and individuals are targeted just as often, often at lower dollar amounts per incident.
What's the single most effective defense against voice-cloning scams?
Verify out-of-band. If a call or video creates urgency around money or sensitive access, hang up and call the person back on a number you already know, rather than one given during the call.
From the Desk
All Technology →More in Technology
Anthropic CEO Advocates Slower AI Development Pace
Anthropic CEO Dario Amodei calls for a controlled pace in AI development. Altman and Musk back the push for increased caution in AI advancements.
Fresh Reporting
Browse All Stories →Latest from The Ledger
High Yield Savings vs Money Market: Choosing the Best Option
Both accounts can park cash safely, but the better choice depends on rate stability, access, and fees. The math changes fast when balances rise or rates fall.
Leave a Comment
Your email address will not be published. Required fields are marked *